Category: IT Security
-
CVE-2022-24348: A Deep Dive into Argo CD’s Critical Path Traversal Vulnerability 🕵️♂️
Hello everyone! This is an IT security information blog that quickly delivers the latest security information for your safe IT environment. 😊 Today, we will delve into a critical vulnerability, CVE-2022-24348, found in Argo CD, a widely used open-source continuous deployment (CD) tool in GitOps environments. 🤔 What exactly is CVE-2022-24348? CVE-2022-24348 is a Path…
-
🛠️ A Broken Piece Can Bring Down the Whole! OWASP #8, Software and Data Integrity Failures
Hello! 👋 Welcome to the OWASP Top 10 Conquest Series. Today, we’ll explore A08:2021-Software and Data Integrity Failures, a new entry in 2021 that emphasizes its critical importance. What if someone secretly erased or altered text on an important document? Or what if a program file you downloaded was tampered with midway and turned into…
-
Linux Server Security: Essential Checklist for Complete Protection! 🐧
Hello! Is your precious Linux server safe and sound today? 🖥️ Even if it looks peaceful on the surface, countless threats lurk unseen. 🕵️♂️ A small security flaw can lead to a major incident. So today, we’ll delve into the Linux/Unix Server Security Essential Diagnostic Checklist to make our servers impregnable. Follow each item carefully…
-
AI for PRD in 10 Minutes? An AI Utilization Guide for PMs 🤖✨
Hello everyone! This blog is for product managers (PMs), planners, and anyone dreaming of a new service. Today, I’d like to talk about PRD (Product Requirements Document), which is often a PM’s most important weapon and sometimes their biggest challenge. Furthermore, I’ll share the key secret to drastically shortening this often tedious and complex PRD…
-
🎭 Turn Your Server into a Hacker’s Puppet! OWASP Top 10, SSRF (Server-Side Request Forgery) Attack
Hello! 👋 This is the final session of our OWASP Top 10 2021 Conquest Series. The much-anticipated 10th spot is A10:2021-SSRF (Server-Side Request Forgery), a very powerful and dangerous attack that newly entered the ranking through a community survey. “What if you manipulated a trusted internal employee to steal secret documents from the boss’s office?”…
-
Safe Without CCTV, OWASP #9 Security Logging and Monitoring Failures
Hello! 👋 In our OWASP Top 10 Conquest Series, today we’ll explore A09:2021-Security Logging and Monitoring Failures, a silent threat that allows attacks to occur unnoticed. What if your home has state-of-the-art locks, but no CCTV to record intruders, or if no one ever checks the recorded footage? 🕵️♂️ ‘Security Logging and Monitoring Failures’ refers…
-
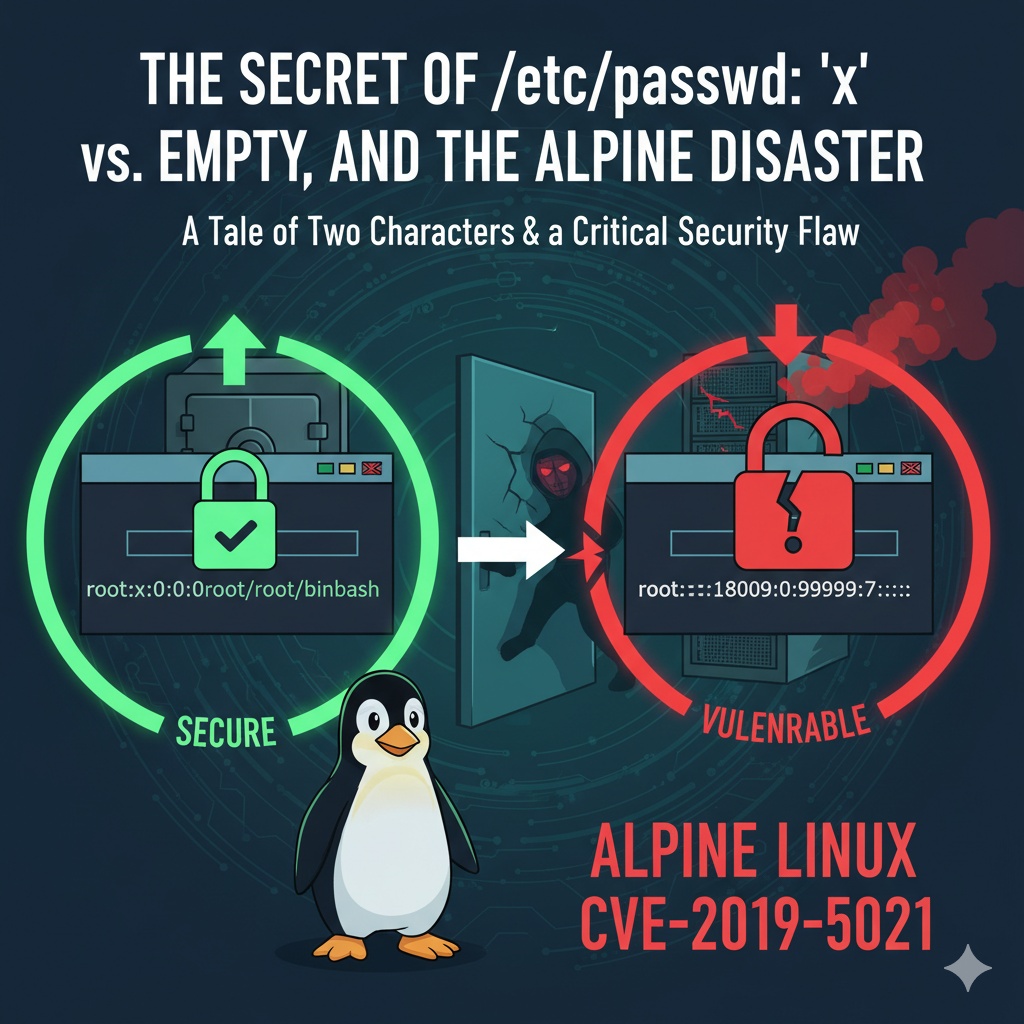
🐧The Secret of /etc/passwd: The Meaning of ‘x’ and ‘Space’, and the Alpine Image Catastrophe!
Hello everyone! Today, we’re going to uncover a small secret hidden within one of Linux system’s core files, /etc/passwd: the meaning of ‘x’ and ‘space’. We’ll explore how this subtle difference led to a massive security disaster, specifically the Alpine Linux image vulnerability incident, explained in an easy-to-understand and detailed manner. 😉 🧐 What exactly…
-
Windows Server Security: Manage Like a Pro! 🛡️ Essential Diagnostic Checklist
Hello! Our company’s Windows servers, responsible for critical data and services, are they truly managed securely? 🧐 Many servers operate with default settings, unknowingly exposing themselves to numerous security threats. Today, we’ve prepared an Essential Windows Server Security Diagnostic Checklist to turn your server into a strong fortress, preventing it from becoming a hacker’s prey.…
-
🔐 Why is ‘top_security_ssl’ attached next to session cookies? (feat. Double Lock Mechanism)
Hello, developers! When you’re surfing the web or developing services, you often find yourself meticulously examining the cookie tab in your browser’s developer tools, don’t you? 🕵️♂️ Have you ever come across an unfamiliar cookie named top_security_ssl among familiar ones like session_id? If you’ve ever wondered, “Isn’t session_id enough to maintain a session? What on…
-
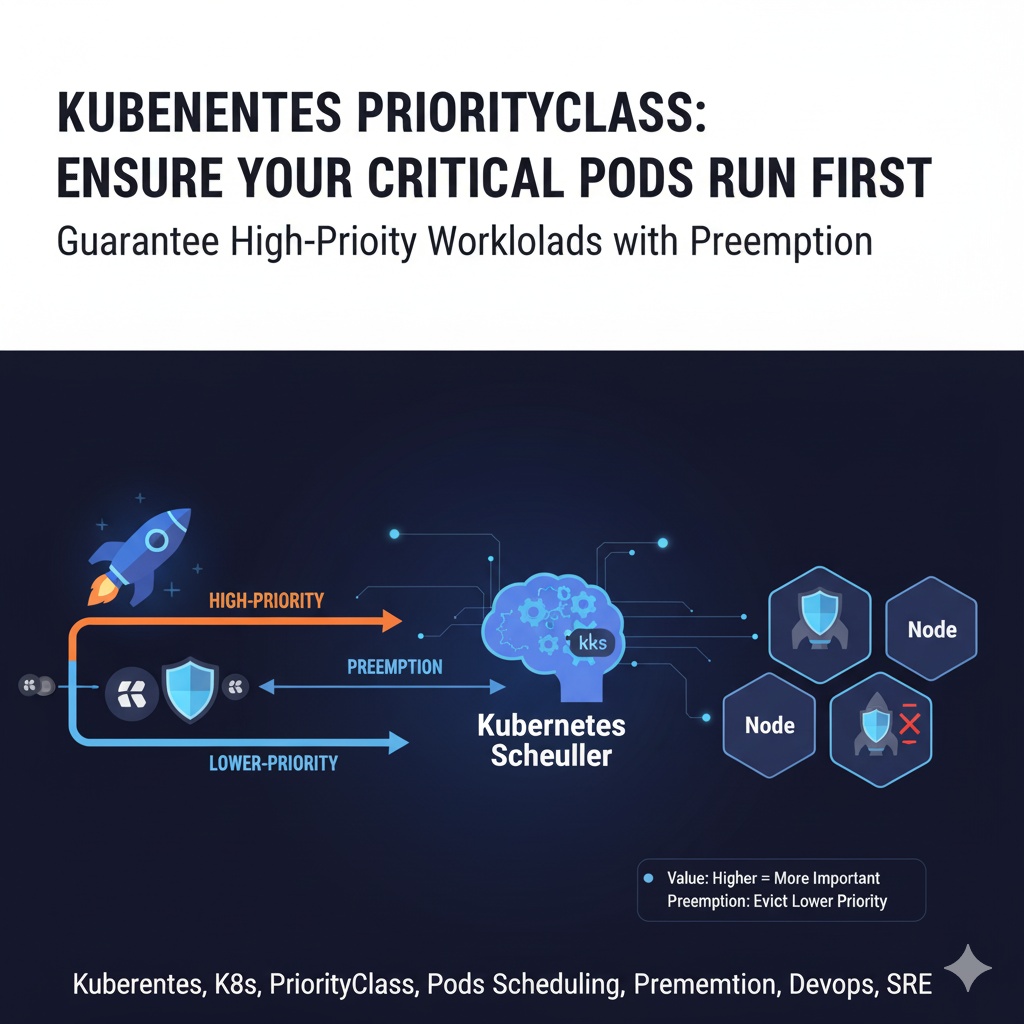
🚀 My Pods are Precious! Setting Importance with Kubernetes PriorityClass
Hello, navigators of the Kubernetes world! 👋 When operating a cluster, there are important workloads where you might think, “This pod must never die!” or “If there’s no space, it must run even if it has to push out other pods!” For example, pods like monitoring systems, logging agents, or core API servers. Today, we’ll…