Category: IT Security
-

OWASP Top 10: A04:2021 Insecure Design and a Deep Dive into STRIDE Threat Modeling 🧐
Hello everyone! 👋 I’m your security guide, here to help you on your journey to secure web development. Today, we’ll explore A04:2021-Insecure Design, a new addition to the 2021 OWASP Top 10, and delve into how to effectively utilize a powerful tool for identifying and preventing such design flaws: STRIDE Threat Modeling. 🤔 What is…
-
🛡️ Let’s Look at Our Service Through the Attacker’s Eyes! A Complete Guide to the OWASP Threat Modeling Process
Hello! 👋 When developing complex software systems today, security is not an option, but a necessity. However, simply writing ‘bug-free code’ is not enough. What’s truly important is to consider in advance, “How can an attacker compromise our service?” The systematic methodology for finding the answer to this very question is ‘Threat Modeling’. Today, based…
-
🏗️ The Wrong First Button, Everything Crumbles! OWASP #4, Insecure Design
Hello! 👋 In our OWASP Top 10 Conquest Series, today we’ll discuss A04:2021-Insecure Design, which newly emerged in 2021 and garnered everyone’s attention. This item doesn’t deal with a single line of code bug, but rather a fundamental problem where the design itself is flawed from the outset. No matter how sturdily a house is…
-
💉 Unmasking Injection: The Fatal Attack Infecting Your Applications
Hello! 👋 Welcome to the OWASP Top 10 series. Today, we’ll delve into A03:2021-Injection, a perennial fixture in the security threat list for nearly 20 years and one of the most dangerous vulnerabilities. ‘Injection’ literally means ‘to inject’. It’s a terrifying attack where a hacker injects malicious code into an application, tricking the system into…
-
🚪 The Open Backdoor: Unpacking OWASP #5 Security Misconfiguration
Hello everyone! 👋 Welcome to the OWASP Top 10 Conquest Series. Today, we’ll be discussing A05:2021-Security Misconfiguration, which has risen from #6 to #5, highlighting its increased importance. Are you still using ‘admin/admin’ as the administrator password for your new router? Such a seemingly minor but critical mistake is the beginning of a ‘security misconfiguration’.…
-
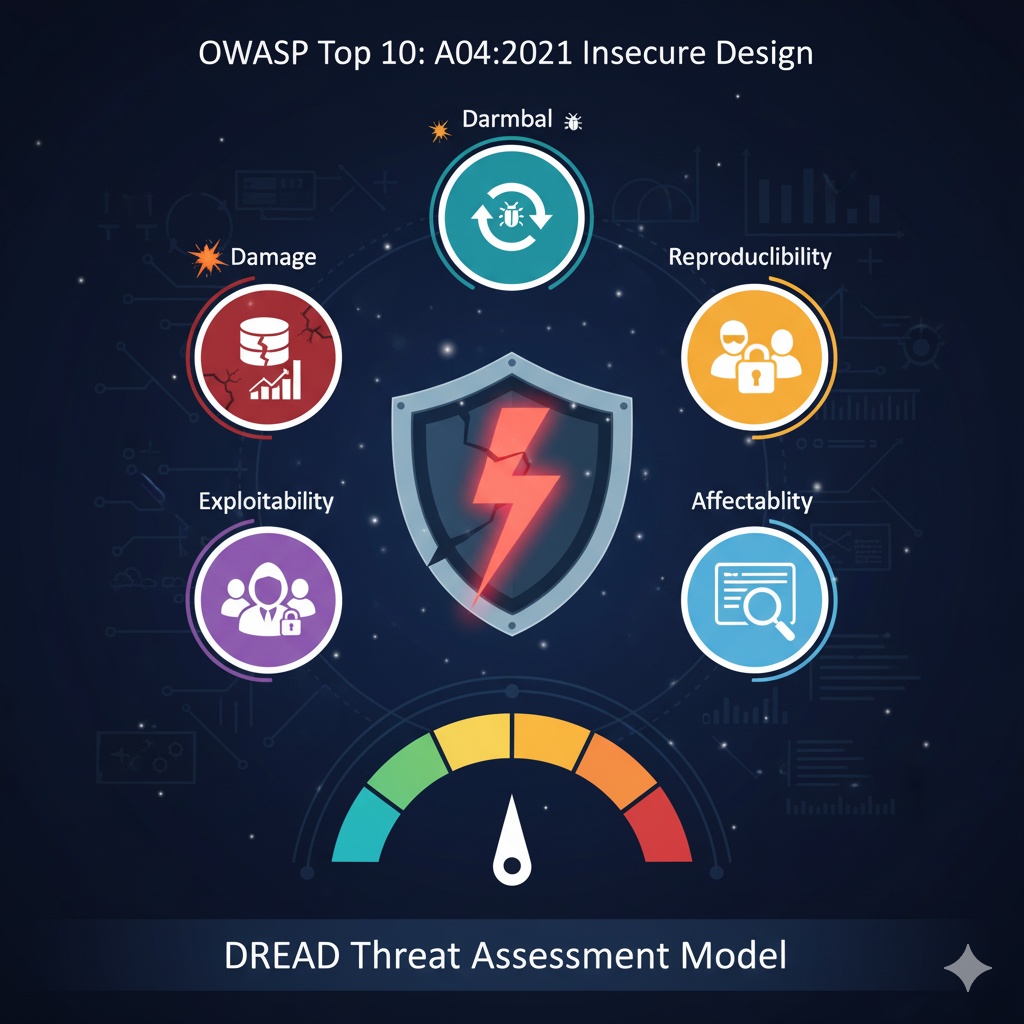
OWASP Top 10: A04:2021 Insecure Design and DREAD Threat Assessment 📊 In-depth Analysis!
Hello everyone! 🌐 Your guide to exploring the world of security vulnerabilities. Today, following up on our last discussion, we will delve deeper into A04:2021-Insecure Design, a core component of the 2021 OWASP Top 10, and provide a detailed explanation of the useful DREAD Threat Assessment Model for evaluating the risk of identified threats. 💡…
-
🚨 Is Your Account Safe? Everything About Credential Stuffing!
Hello! This is your information security guardian, protecting your digital safety. 👋 Today, we’re going to thoroughly and easily break down everything from A to Z about a subtle hacking technique that can steal your personal information without you even knowing: Credential Stuffing. 🕵️♂️ 🤔 What exactly is Credential Stuffing? Credential stuffing can be defined…
-
🔑 Useless if the lock is flimsy! OWASP #7, Unpacking Identification and Authentication Failures
Hello! 👋 In our OWASP Top 10 Conquest series, today we’ll explore A07:2021-Identification and Authentication Failures, which was more comprehensively renamed from “Broken Authentication” in 2017. What if your front door has a sturdy lock, but that lock is too common (easy password), or your key bundle is exposed to anyone? 😱 Similarly, ‘Identification and…
-
🦠 A Time Bomb Hidden in My Service! OWASP #6, Vulnerable and Outdated Components
Hello everyone! 👋 Welcome to the OWASP Top 10 Conquest Series. Today, we’ll be exploring A06:2021-Vulnerable and Outdated Components, whose name has become even clearer in the 2021 version. The wonderful service you’ve developed – does it perhaps harbor a time bomb that could explode at any moment? 💣 Rather than writing all the code…
-
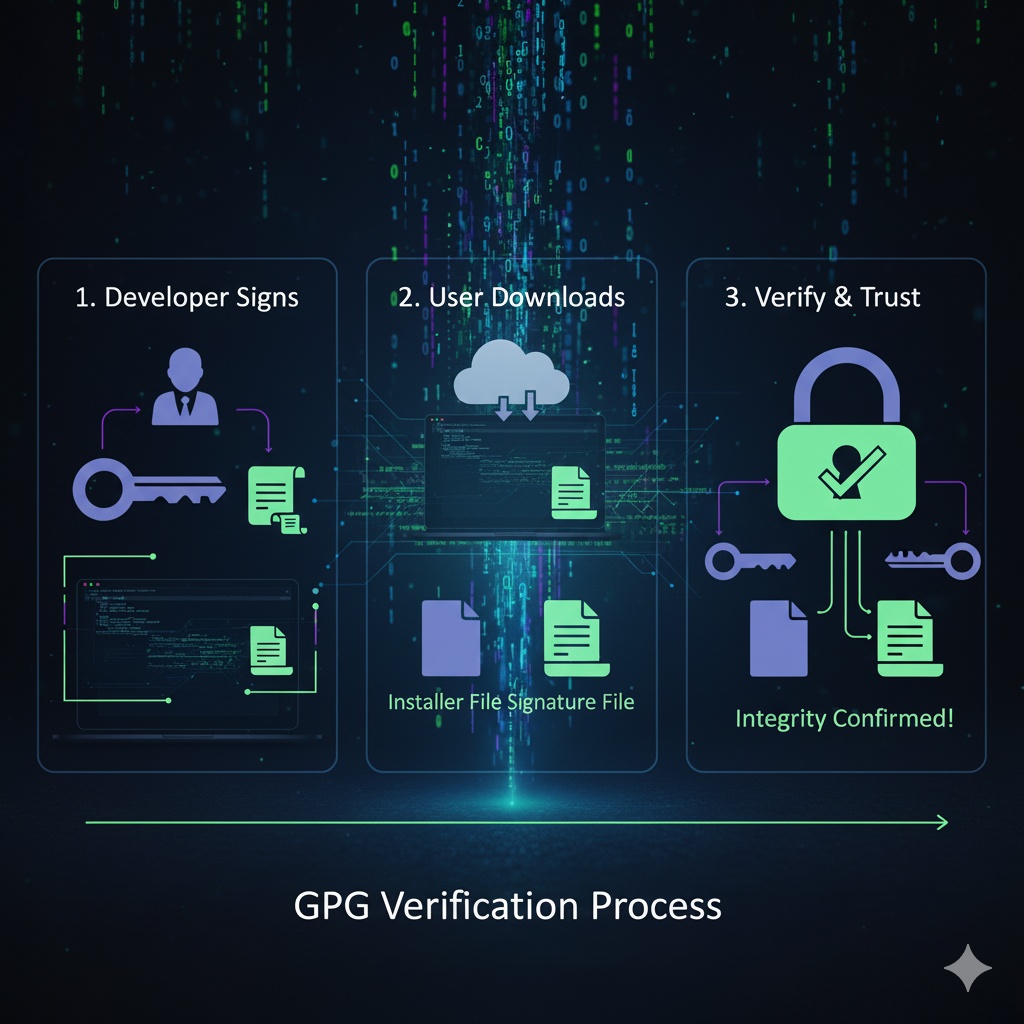
📥 Downloaded Files: Are They Really Safe? Unpacking Integrity Verification with GPG 🧐
Hello! 😄 Today, when you download files from the internet, we’re going to easily and thoroughly explore a method called ‘integrity verification’ to check if the file is truly the original created by the developer, and if no one has tampered with it in between. Even if you’re not a developer, general users can easily…