Hello! If you operate multiple Linux servers, you’ve probably thought at some point, “I wish I could use files from this server directly on that server.” Copying files with scp every time is cumbersome, and synchronizing with rsync also has its limitations.
This is where NFS (Network File System) comes in handy! With NFS, you can mount a directory from another networked server and use it as if it were a local directory on your own computer. It’s like connecting a USB drive over the network. 😉
Today, we’ll explore the three most basic steps to configure an NFS server and share a specific folder with other computers.
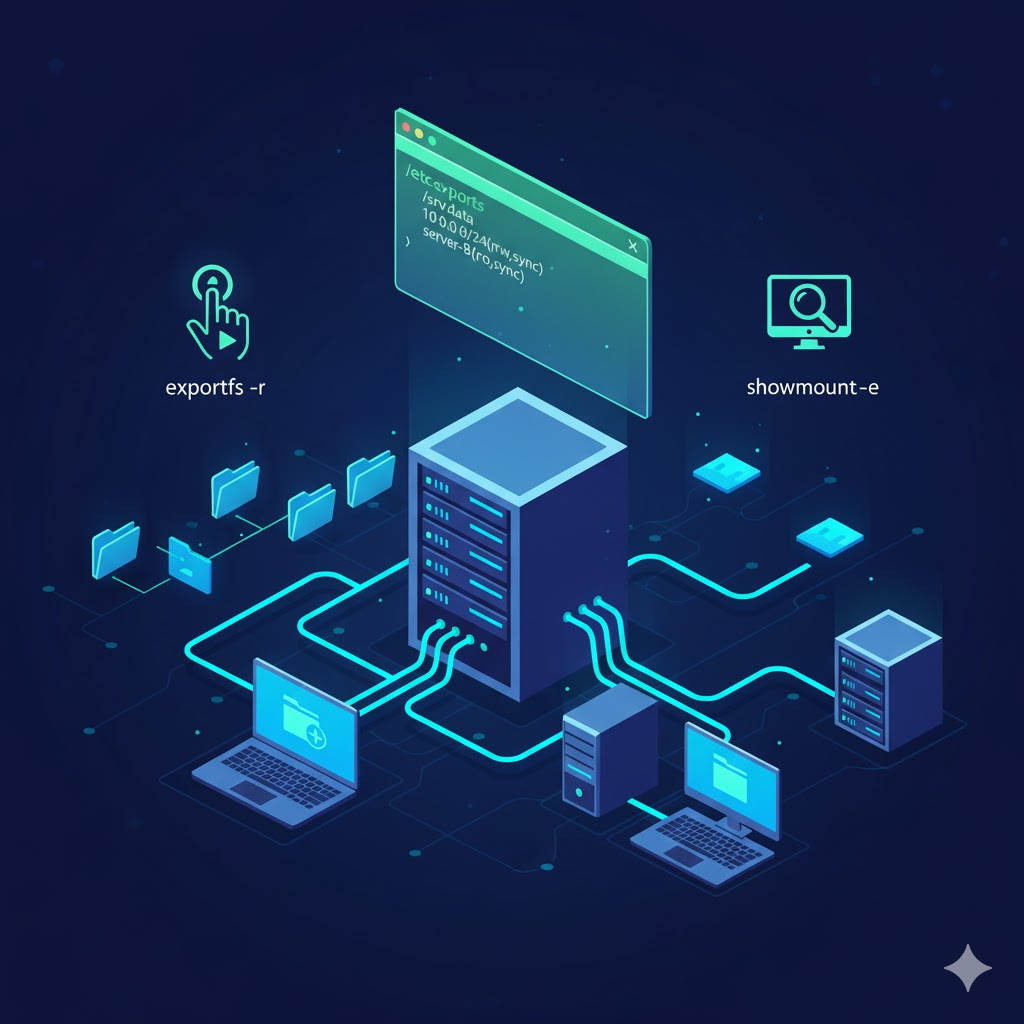
Step 1: Define Sharing Rules (/etc/exports file) ✍️
The heart of NFS server configuration is the /etc/exports file. This file is a list of rules that define “what directory (What) to share, with whom (Whom), and with what permissions (How).”
The basic format of a rule is as follows:
[공유할 디렉터리 경로] [허용할 클라이언트]([옵션])Let’s take a closer look at each item:
- ① Directory Path to Share
- Enter the absolute path of the folder you want to share over the network. (e.g., /srv/data)
- ② Allowed Clients
- Specify who can access this directory. You can specify in various formats:
- Single IP: 192.168.1.100 (Allows only one specific computer)
- IP Range: 10.0.0.0/24 (Allows an entire specific network range)
- Hostname: client-pc.example.com
- Allow All: * (Allows all clients, caution advised for security!)
- ③ Options
- These are detailed settings for the sharing method. Let’s look at some of the most important options:
- ro: **Read-Only** shares. Clients can view or copy files, but cannot modify or delete them. (Default)
- rw: Allows both **Read and Write**. Clients can freely modify and create files.
- sync: Responds to the client only after data is fully saved to disk upon file changes. This increases stability but may cause a slight performance degradation. (Default and recommended)
- no_root_squash: A very important security option. By default, when a client’s root user writes files to the server, NFS forcibly maps them to the unprivileged nfsnobody user (this is called root_squash). This option disables this feature, allowing the client’s root user to have root privileges on the server as well. This grants powerful permissions and should only be used when absolutely necessary.
Combined Example: If you want to share the /srv/data directory with clients in the 10.0.0.0/24 range with read-write permissions, and with a host named server-B with read-only permissions, you can add the following to the /etc/exports file:
/srv/data 10.0.0.0/24(rw,sync) server-B(ro,sync)Step 2: Apply Settings (exportfs command) 🔄
Modifying and saving the /etc/exports file does not immediately apply the settings. You need to tell the NFS service to re-read the changed rules. The command used for this is exportfs.
sudo exportfs -r- The -r option re-reads the /etc/exports file to update the current share list to the latest state. It’s very useful as it allows you to apply settings immediately without needing to restart the NFS service.
Step 3: Verify Share Status (showmount command) ✅
It’s essential to verify that the settings have been applied correctly. The showmount command shows which directories the NFS server is currently sharing and with whom.
# Check the share list of my server (localhost).
showmount -e localhost
If you run this command and see the content you added to /etc/exports in Step 1, then the configuration has been successfully completed!
Export list for localhost:
/srv/data 10.0.0.0/24,server-B
In Conclusion
How was it? Simpler than you thought, right?
- Write sharing rules in the /etc/exports file,
- Apply settings with the exportfs -r command, and then
- Verify with the showmount -e command!
If you remember these three steps, you can freely configure file sharing using NFS on Linux. All that’s left is to connect and use this shared directory on the client server with the mount command. We’ll cover that in more detail next time.
Tags: NFS, Linux, Server, Network, File Sharing, DevOps, System Engineering, IT Infrastructure
Leave a Reply